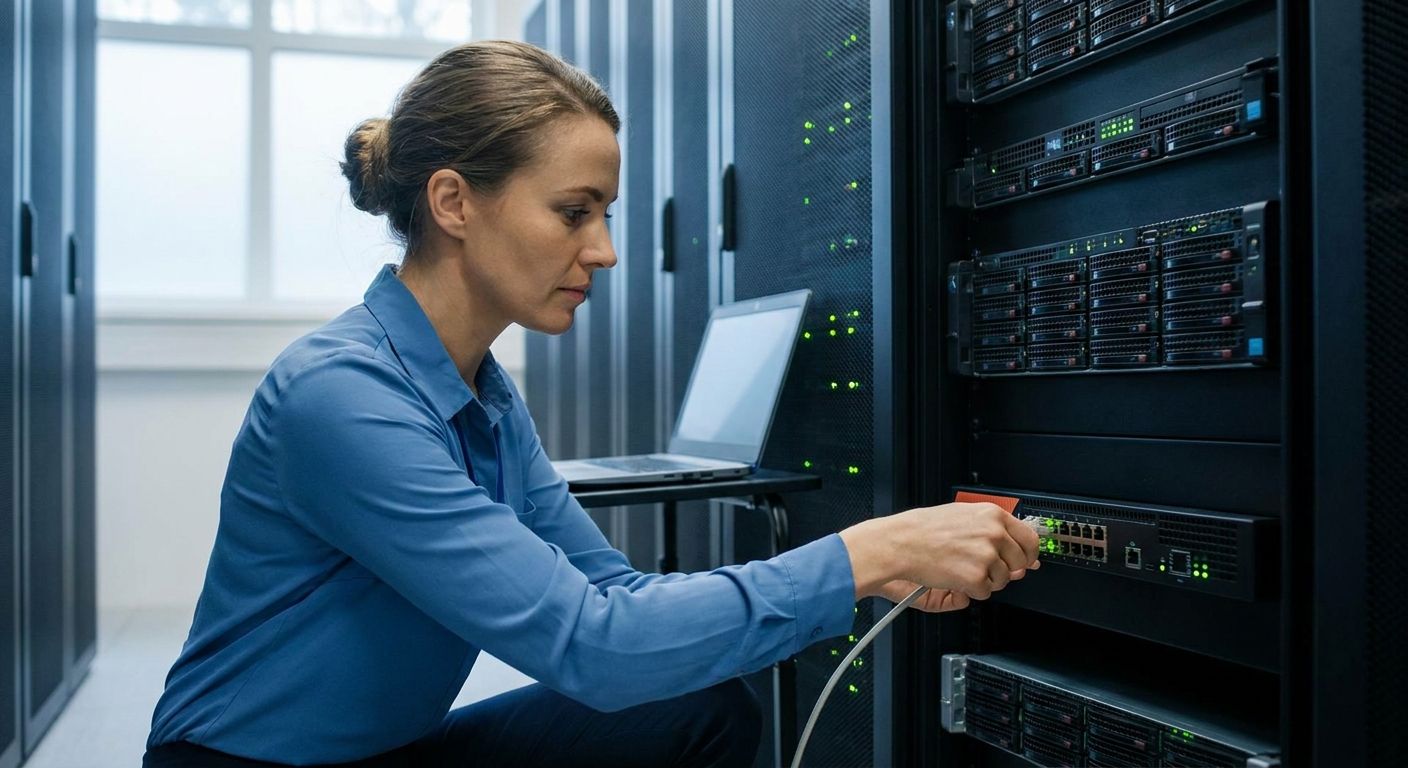
Securing a business network with a firewall in 2026 means deploying a next-generation firewall (NGFW) at the perimeter, segmenting internal traffic into separate VLANs, and pairing that firewall with endpoint antivirus and VPN access control — a single consumer router with default settings does not count as protection. The visible cost is the appliance itself; the hidden cost is the ongoing rule management, firmware patching, and log review that most small businesses skip until something goes wrong.
- A next-generation firewall (NGFW) with VLAN segmentation is the 2026 baseline for how to secure a business network with a firewall.
- Stateful-only firewalls skip deep packet inspection and miss most modern malware traffic.
- POS terminals, guest Wi-Fi, and office devices need separate zones behind the same firewall.
- Firmware left unpatched for 6+ months is the single most common cause of firewall breaches.
- Voll pairs firewall setup with network install and Primavera/Cegid-integrated systems for Portuguese SMEs.
Why this matters
A firewall is the single control point between your business data and the open internet, and in 2026 it's also the control point between your POS system, your guest Wi-Fi, and whatever a customer's laptop is carrying. Most breaches at small and mid-size businesses in Portugal don't start with a sophisticated attack — they start with an open port, a default admin password, or a flat network where a compromised guest device can reach the same switch as the accounting workstation. Getting the firewall right once removes that exposure permanently; getting it wrong means rebuilding trust with clients and possibly reporting a data incident.
How to secure a business network with a firewall
The process is the same whether you run a single retail store or a multi-branch operation, just scaled differently:
- Map the network first. List every device, connection, and data flow: POS terminals, servers, office laptops, IP cameras, guest Wi-Fi. You can't segment what you haven't mapped.
- Pick a firewall sized to your throughput, not just your headcount — a 10-person office running video calls and cloud backup needs more inspection capacity than a 10-person office that only browses email. A next-gen firewall built for small business network security handles both scenarios if sized correctly.
- Create VLANs and zone-based rules. Separate POS/payment traffic, staff workstations, guest Wi-Fi, and IoT devices (cameras, printers) into distinct segments so a compromise in one zone can't reach the others.
- Turn on deep packet inspection (DPI) and IPS/IDS. These features distinguish an NGFW from a basic stateful firewall and catch malware hidden inside otherwise-allowed traffic like HTTPS on port 443.
- Set up VPN for remote staff and branch offices instead of exposing internal services directly to the internet. For chains with more than one location, multi-branch VPN connectivity keeps stores talking to head office without opening the firewall wide.
- Layer endpoint antivirus on every device. The firewall stops network-level threats; antivirus stops what arrives through USB drives, email attachments, or an already-infected laptop.
- Log everything and review weekly. A firewall generates data that's useless if nobody looks at it — set a recurring 15-minute weekly check on blocked-traffic alerts.
- Patch firmware monthly. Vendors ship security patches for a reason; unpatched firewalls are consistently the entry point in documented small-business breaches.
Firewall types compared
| Type | What it does | Best for |
|---|---|---|
| Stateful firewall | Tracks connection state, filters by port/IP | Very small offices with basic internet-only needs — Wait, most SMBs outgrow it fast |
| Next-generation firewall (NGFW) | Adds DPI, application awareness, IPS/IDS | Retail, professional services, offices with POS or remote staff — Buy |
| UTM (unified threat management) | NGFW plus antivirus and content filtering in one box | Small teams wanting one appliance to manage instead of three — Buy |
Next-generation firewall (NGFW): the 2026 standard for most SMBs
An NGFW inspects traffic at the application layer, not just the port and protocol, which means it can tell the difference between legitimate HTTPS traffic to a banking site and malware phoning home over the same port 443. This is now the minimum spec any business handling card payments, customer data, or remote staff access should run in 2026. Setup takes longer than a basic router because you're defining zones and rules instead of accepting defaults — that's the trade-off for real protection. Verdict: Buy for any business with more than a handful of devices or any card-payment traffic.
UTM firewall: firewall, antivirus, and VPN in one box
A UTM appliance bundles the NGFW engine with antivirus scanning and VPN termination, which simplifies management for a team without dedicated IT staff. The trade-off is a single point of failure and less flexibility to upgrade one function independently. Verdict: Buy for single-location businesses that want one vendor and one support line instead of three separate tools.
Stateful firewall: basic perimeter filtering
A stateful firewall tracks whether traffic belongs to an established connection but doesn't inspect the contents of that traffic — it's the level built into most consumer routers. It stops random scanning and unsolicited inbound connections but misses malware riding on allowed ports. Verdict: Wait — fine for a home office, not enough for a business network in 2026.
Why firewall setup varies from one business to another
No two networks need the same configuration. The variables that change your setup:
- Number of physical locations — single stores need one firewall; chains need site-to-site VPN and centralized rule management.
- Payment card handling — any POS or card terminal traffic needs its own VLAN, isolated from office and guest networks.
- Guest Wi-Fi volume — cafes, hotels, and retail floors with heavy guest traffic need strict isolation so a guest device can never reach the internal LAN.
- IoT and camera density — IP cameras and smart devices are common attack entry points; putting them on their own segment behind managed switches built for growing offices limits the blast radius if one gets compromised.
- Remote and hybrid staff — every remote worker is a potential entry point unless VPN access is enforced at the firewall, not left to individual laptop settings.
- Compliance obligations — businesses handling health, legal, or financial records typically need logging and retention policies the firewall must support.
Get your network security setup right
Firewall, VLAN segmentation, and installation for Portuguese businesses.
Do I need a firewall if I already run antivirus?
Yes — antivirus and a firewall solve different problems and neither replaces the other. Antivirus catches malicious files once they've already reached a device; a firewall stops network-level attacks and unauthorized connections before they get that far, which is why both should run together in any 2026 setup.
Can a router replace a business firewall?
A consumer router cannot replace a business firewall because most routers only do basic stateful filtering with no application-layer inspection, no VLAN segmentation, and no VPN management built for multiple users. Businesses handling payment data or remote access need the deeper inspection and zone control an NGFW or UTM provides.
How often should firewall rules be reviewed?
Firewall rules should be reviewed at least quarterly, with logs checked weekly, because rule sets accumulate outdated entries as staff, vendors, and devices change over time. A rule left open for a vendor that no longer works with you is a door nobody remembers unlocking.
FAQ
What's the best firewall type for a small retail store in 2026?
A next-generation firewall (NGFW) is the best fit for most small retail stores in 2026 because it segments POS traffic from guest Wi-Fi and inspects traffic at the application layer, not just the port.
Is a UTM firewall better than a standalone NGFW?
A UTM firewall bundles antivirus and VPN with the firewall engine, which suits single-location businesses without dedicated IT staff; a standalone NGFW gives more flexibility for businesses that want to upgrade each function separately.
How much network segmentation does a small business actually need?
At minimum, separate POS/payment traffic, staff workstations, and guest Wi-Fi into three VLANs behind the firewall — more locations or IoT devices call for additional segments.
Does a firewall protect remote workers too?
Yes, when remote access runs through a firewall-managed VPN instead of exposed internal services, remote workers get the same inspection and access control as staff on-site.
How often should firewall firmware be updated?
Firewall firmware should be updated monthly at minimum, since vendors ship security patches on a regular cycle and unpatched firmware is a common breach entry point.
Can one firewall cover multiple business locations?
One central firewall combined with site-to-site VPN can cover multiple locations, letting branches share rules and monitoring instead of each site managing its own device independently.
What happens if a business skips network segmentation?
Without segmentation, a single compromised device — a guest laptop or an infected IoT camera — can reach the same network as POS systems and staff workstations, turning a minor incident into a full breach.
Do I need IT support to configure a business firewall?
Configuring zones, VLAN rules, and VPN correctly takes networking knowledge most small businesses don't have in-house, which is why installation support alongside the hardware purchase saves rework later.
One last thing
The most overlooked step isn't buying the firewall — it's putting IP cameras and other IoT devices on their own VLAN instead of the same segment as office workstations. Cameras run outdated firmware for years and rarely get patched, making them one of the quieter entry points into an otherwise well-secured network in 2026.